SIEM and 24/7 Threat Monitoring for Queensland Businesses
Loginet’s SIEM and threat monitoring collects security events from across your systems and watches them 24/7, so suspicious activity gets spotted and acted on quickly. One team, no handoffs, and clear reporting.
- 20+ IT experts certified in AWS, Microsoft, Cisco, Palo Alto, Fortinet and CEH
- 4+ years supporting Queensland small and medium businesses
- AWS Partner & Microsoft Azure Partner
Technologies We Work With
What Is SIEM and 24/7 Threat Monitoring?
SIEM threat monitoring is a service that collects security logs from across your systems, analyses them for signs of attack and alerts our team so threats can be investigated quickly, with 24/7 monitoring.
Day to day, a SIEM (security information and event management) platform gathers events from sources such as Microsoft 365, firewalls, servers and endpoints. It correlates those events to spot patterns, such as unusual sign-ins or suspicious activity, that individual tools may miss. Alerts are reviewed by our team and handled in line with the agreed process.
For small and medium businesses, the challenge is visibility. Security tools generate alerts, but nobody has time to watch them all. SIEM threat monitoring brings those signals together so real threats aren’t lost in the noise.
Signs You Need SIEM Threat Monitoring
SIEM monitoring is worth considering when:
- Your cyber insurer or customers ask how you detect security incidents
- You have security tools but nobody reviews their alerts regularly
- You couldn't easily tell whether an account had been compromised
- You need to keep security logs for audits or investigations
- You handle sensitive data and need better visibility of access
What's Included / How It Works in Practice
Our SIEM service is scoped to your systems and risks. It typically includes:
- Log source onboarding: Connection of agreed sources, such as Microsoft 365, firewalls, servers and endpoints.
- Detection rules: Rules tuned to your environment to reduce false alarms.
- 24/7 monitoring: Alerts monitored around the clock.
- Alert review and notification: Alerts investigated and escalated to you under the agreed process.
- Log retention: Security logs kept for an agreed period to support investigations.
- Reporting: Regular summaries of alerts, trends and recommendations.
Who SIEM and 24/7 Threat Monitoring Is For
SIEM and threat monitoring suit businesses that need more visibility than antivirus alone provides.
- Businesses holding sensitive customer or financial data
- Organisations with security requirements from customers or insurers
- Businesses using Microsoft 365 that want sign-in threats watched
- Companies that want monitoring without building a security team
Benefits of SIEM and 24/7 Threat Monitoring With Loginet
SIEM and threat monitoring give you eyes on your environment around the clock, and a team ready to act.
Threats seen across your whole environment
Correlating events from many sources reveals attacks a single tool would miss, such as unusual sign-ins followed by mailbox rule changes. You get a joined-up view of security, not separate tools working in isolation.
24/7 monitoring
Security events are monitored 24/7, so suspicious activity overnight or on weekends isn't left until Monday. Attackers often strike after hours, and someone is watching when they do.
One team, no handoffs
The team that manages your IT also reviews your security alerts, so response is faster and context isn't lost. No time is lost explaining your environment to a third party.
Evidence for audits
Regular reports show what was monitored, detected and done, which supports compliance and insurance. You can show what's being watched and how incidents were handled.
Our SIEM and 24/7 Threat Monitoring Services
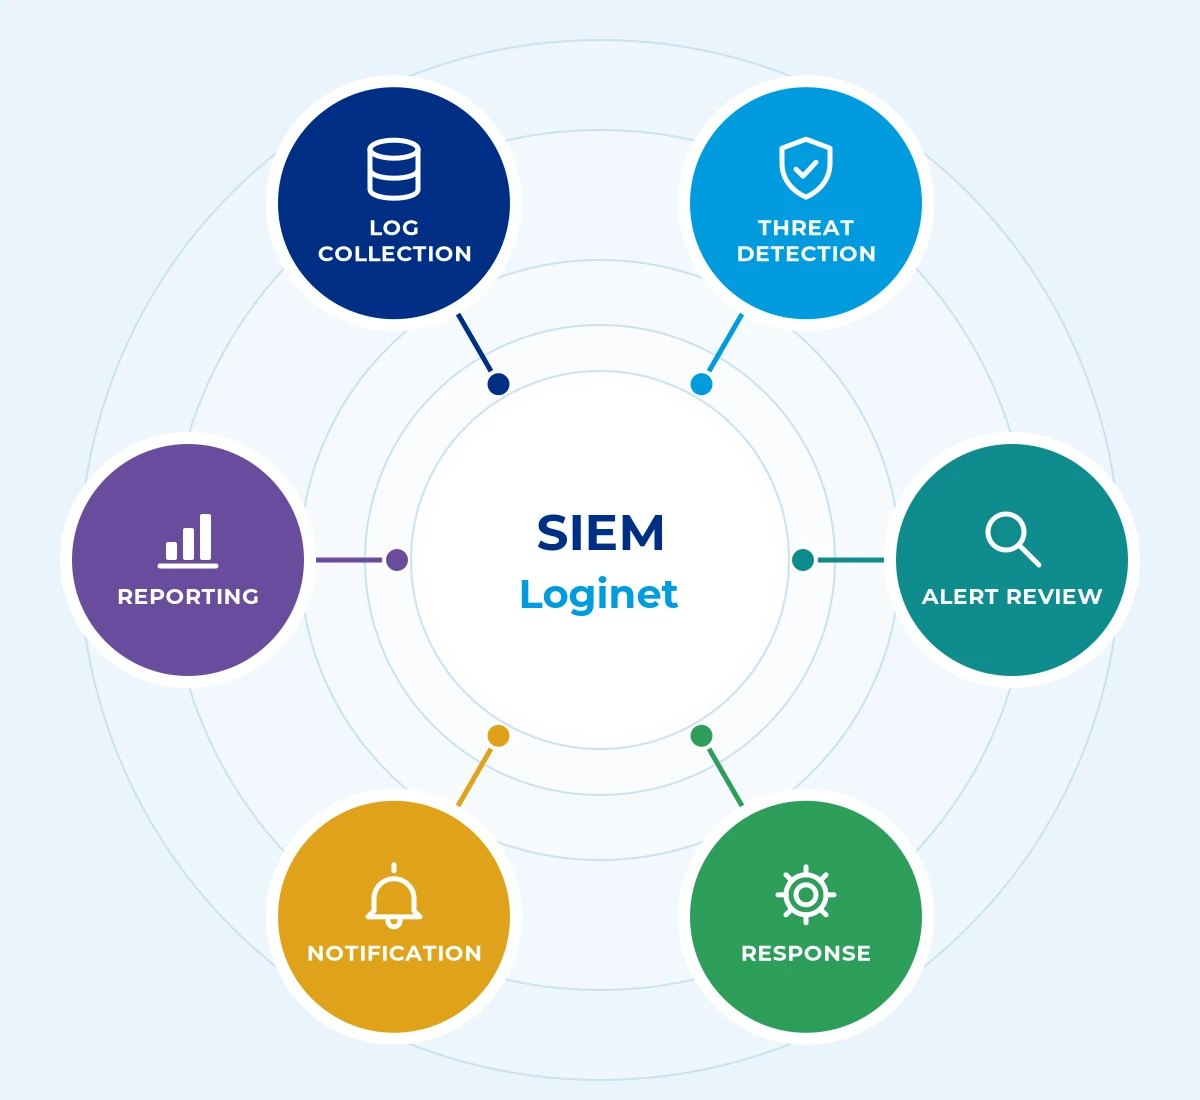
Loginet’s SIEM and 24/7 threat monitoring covers six core areas, scoped to suit your business so you only pay for what you need.
Log collection
Events gathered from endpoints, servers, firewalls and Microsoft 365 into a central platform. Security-relevant events are kept in one place for analysis.
Response guidance and remediation support
When an issue is confirmed, we respond with guidance and remediation support, in line with the agreed process, so you know exactly what to do next.
Threat detection
Correlation rules and analytics highlight suspicious patterns and known attack techniques. Rules are tuned to your environment, so real threats stand out.
Notification
You're told what happened, what it means and what was done, in plain English. You always know what happened and what's being done.
Alert review
Engineers review alerts to separate genuine threats from noise. You're only contacted about what genuinely needs attention.
Reporting
Regular summaries for management, auditors and insurers. Trends over time show whether your security is improving.
How We Deliver SIEM and 24/7 Threat Monitoring
Every SIEM and 24/7 threat monitoring engagement follows four clear steps, so you know the scope, timeline and cost before work starts.
1. Security review
We review your environment and risks, so monitoring focuses on what matters most.
2. Onboard
We connect your log sources to the SIEM, with minimal disruption to your systems.
3. Tune
We tune detection rules so you get meaningful alerts, not noise.
4. Monitor and report
We monitor 24/7 and report regularly, so you know what's happening across your environment.
SIEM and 24/7 Threat Monitoring Across the Gold Coast, Toowoomba, Brisbane & Queensland
Loginet delivers SIEM and 24/7 threat monitoring from our Toowoomba head office and our Bundall office on the Gold Coast, with onsite support across Queensland and service available in other Australian states. Brisbane businesses are supported remotely, with onsite visits when needed. We support SIEM and threat monitoring for businesses across South East Queensland, with managed IT in Toowoomba from our head office, managed IT on the Gold Coast from our Bundall office, and managed IT in Brisbane delivered remotely and on site from our Toowoomba and Bundall teams.
Gold Coast
Our Bundall office supports businesses across Southport, Surfers Paradise, Broadbeach, Robina and the wider Gold Coast.
Toowoomba
Our head office serves Toowoomba and the Darling Downs with local, onsite support.
Brisbane
We support Brisbane businesses remotely, with onsite visits arranged when your project needs them.
Regional Queensland
We provide onsite support across Queensland, with service available in other Australian states.
Why Choose Loginet for SIEM and 24/7 Threat Monitoring
Loginet runs SIEM as part of your IT, not as a separate black box.
- CEH-certified engineers: Security skills alongside infrastructure knowledge.
- 24/7 monitoring: Security events watched around the clock.
- Context-aware: We know your systems, so alerts are judged faster.
- Local: Toowoomba and Gold Coast offices.
SIEM and 24/7 Threat Monitoring FAQs
Here are straight answers to the questions we hear most. If yours isn’t covered, book a free 30-minute strategy call.
SIEM stands for security information and event management. It collects logs from across your environment and correlates them to detect security threats.
Antivirus focuses on known malware on individual devices. SIEM looks across your whole environment for suspicious patterns, such as unusual sign-ins.
Typical sources include endpoints, servers, firewalls and Microsoft 365. The scope is agreed during onboarding.
We detect and review the alert, notify you, respond with guidance and remediation support, and report, following an agreed process.
Yes. Security events are monitored 24/7.
We start with a security review, provide a proposal, onboard your log sources and tune detections to your environment.
Yes. Brisbane businesses are supported remotely, with onsite visits arranged when needed, from our Toowoomba head office and Bundall (Gold Coast) office.
Cost depends mainly on the number of log sources, the volume of data, log retention requirements and the scope of alert handling.
Onboarding log sources can start quickly, but tuning detection rules to your environment usually takes a few weeks.
SIEM collects and correlates logs from many sources. EDR detects and responds to threats on individual devices. MDR is a managed service that typically combines detection tools with a dedicated response team. Loginet provides SIEM with 24/7 monitoring; it is not an MDR service.
Endpoint protection secures devices, but it doesn’t see everything, such as Microsoft 365 sign-ins or firewall events. SIEM brings those sources together for broader visibility.
It helps but doesn’t make you compliant on its own. Monitoring supports the logging expectations at Maturity Level Two and helps you answer insurer questions about 24/7 monitoring, while prevention controls such as patching and MFA still need to be in place.
If you hold customer data, rely on Microsoft 365 and nobody watches security alerts after hours, yes. Attacks often start overnight or on weekends, when no one in a small business is watching.
Book Your Free 30-Minute Strategy Call
The quickest way to get started is a free 30-minute strategy call. We’ll talk through your setup and goals and give you clear next steps, with no obligation. Prefer to write? Send us a message instead.
Let's talk about your IT
Book a free 30-minute strategy call with our team, or send us a message. No obligation, no hard sell, just straight answers about your IT, cloud and telecom.
Prefer to call?
Sales: Mon–Fri 8:30am–5pm AEST. Existing clients: 24/7 support on the same number.
Book a free 30-minute call
30 minutes · Video or phone · Times shown in Australia/Brisbane (AEST)
Calendar not loading? Open the booking page in a new tab (opens in a new tab)