IT Compliance and Governance Services for Queensland Businesses
Loginet helps small and medium businesses meet IT compliance obligations without the confusion. We assess your risks, write practical policies, align controls with frameworks such as the Essential Eight and help you get audit-ready.
- 20+ IT experts certified in AWS, Microsoft, Cisco, Palo Alto, Fortinet and CEH
- 4+ years supporting Queensland small and medium businesses
- AWS Partner & Microsoft Azure Partner
Technologies We Work With
What Is IT Compliance and Governance Services?
IT compliance and governance is the set of policies, processes and controls that make sure your technology is managed responsibly, meets legal obligations such as the Privacy Act and can be evidenced when customers, insurers or auditors ask.
Day to day, that means identifying the obligations that apply to you, keeping asset and risk registers, writing IT policies staff can follow, preparing for data breaches under the Notifiable Data Breaches scheme, and gathering the evidence you need for audits and insurance questionnaires.
Small and medium businesses increasingly face compliance questions from customers, insurers and government contracts. IT compliance and governance gives you a clear framework and documentation, without the overhead of a full-time compliance team. We provide practical IT guidance, not legal advice.
Signs You Need IT Compliance and Governance
It’s time to formalise compliance when:
- You're unsure whether the Privacy Act applies to your business
- You don't have a plan for responding to a data breach
- Customers or insurers ask for IT policies you don't have
- There's no up-to-date register of your systems and data
- Audit preparation is a last-minute scramble
What's Included / How It Works in Practice
Our compliance and governance work is scoped to your obligations. It typically includes:
- Obligations review: Identifying the legal, contractual and insurance requirements that apply.
- Privacy and data breach readiness: Practical steps for handling personal information and responding to eligible data breaches under the NDB scheme.
- Asset and risk registers: Records of systems, data and risks, with owners and actions.
- IT policies: Clear policies for acceptable use, access, passwords and data handling.
- Evidence pack: Documentation to support audits, contracts and insurance questionnaires.
- Ongoing reviews: Regular checks to keep policies and registers current.
- Staff compliance awareness: Practical guidance so staff understand their responsibilities under your policies and privacy obligations.
Who IT Compliance and Governance Services Is For
IT compliance and governance support helps businesses facing growing security and privacy expectations. If you’re not sure which requirements apply, we’ll help you work it out.
- Businesses asked to complete security questionnaires
- Organisations handling personal information
- Companies preparing for an audit or certification process
- Leadership teams wanting clear IT policies
Benefits of IT Compliance and Governance Services With Loginet
Good governance makes compliance easier, audits calmer and risk decisions clearer.
Ready when auditors ask
Evidence, policies and records are organised ahead of time, so audits are far less stressful. Your team spends less time scrambling for documents.
Risks managed, not ignored
A risk register and treatment plan focus effort on what matters. Leadership can see risks and decisions in one place.
Policies people understand
Plain-English IT and security policies staff can actually follow. Policies match how your business actually works.
Compliance that stays current
Ongoing monitoring keeps controls and evidence up to date. Changes in your business or regulations are reflected quickly.
Our IT Compliance and Governance Services
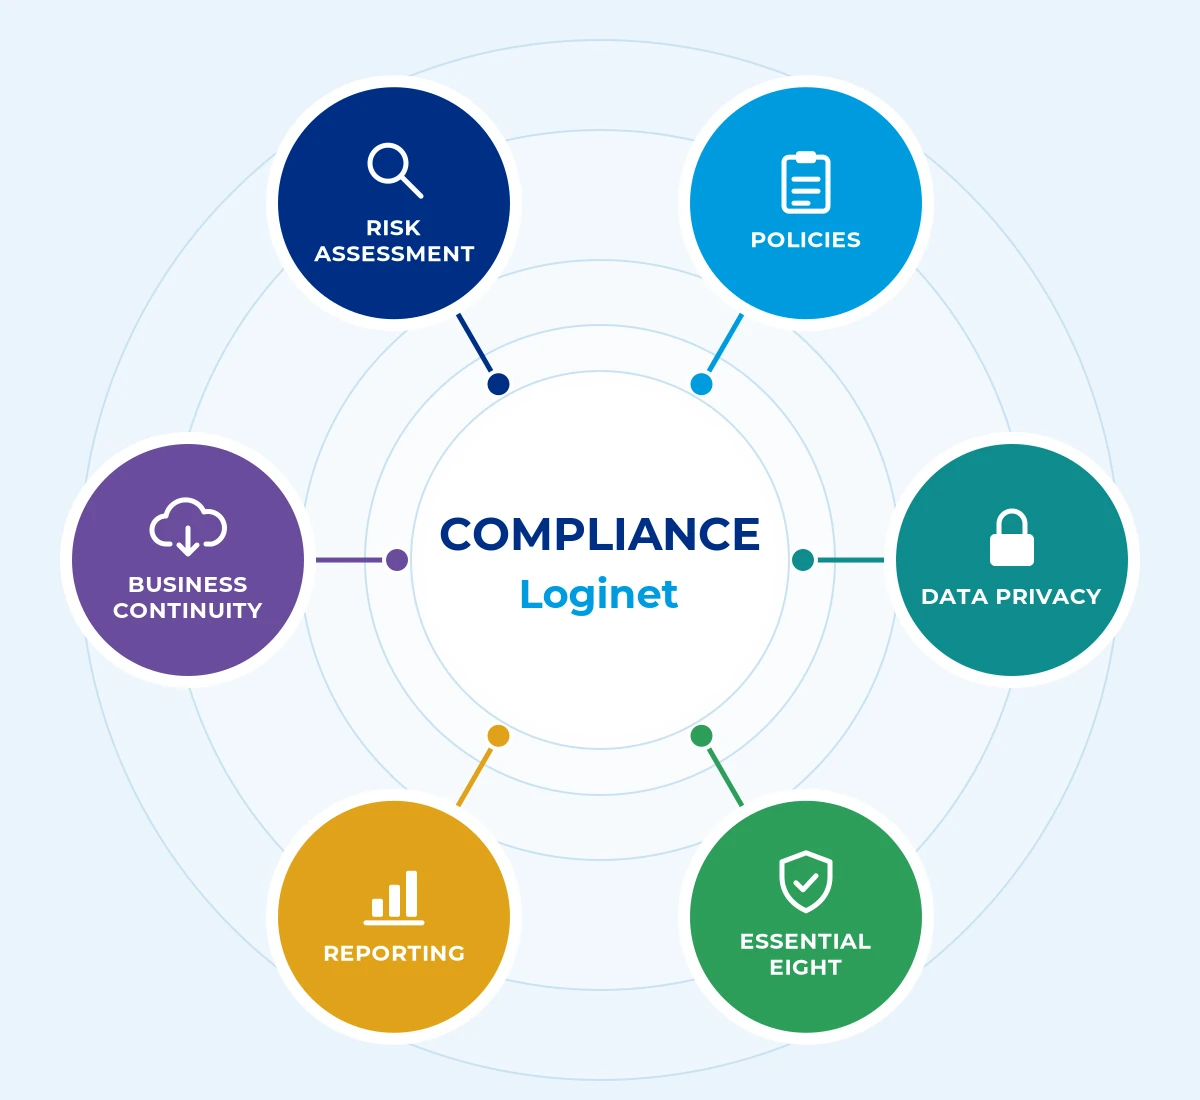
Loginet’s IT compliance and governance services covers six core areas, scoped to suit your business so you only pay for what you need.
Risk assessment and management
Identify, rate and treat IT risks. A living risk register guides decisions and budgets.
Essential Eight alignment
Maturity assessment and uplift. Progress is tracked against a recognised Australian framework.
Policy development
IT, security, acceptable-use and access policies. Each policy is practical, approved and easy for staff to follow.
Compliance monitoring and reporting
Track controls and evidence over time. Evidence is collected continuously, not just at audit time.
Data privacy compliance
Support with Australian privacy obligations. Personal information is handled and protected appropriately.
Business continuity planning
Plans to keep operating after a disruption. Everyone knows their role if something goes wrong.
How We Deliver IT Compliance and Governance Services
Every IT compliance and governance services engagement follows four clear steps, so you know the scope, timeline and cost before work starts.
1. Identify obligations
We identify the obligations that apply to your business, so effort goes where it's needed.
2. Assess
We assess your current policies and controls against those obligations.
3. Close gaps
We close the gaps with practical policies and controls, so compliance becomes part of how you work.
4. Monitor
We review and monitor regularly, so you're ready whenever someone asks for evidence.
IT Compliance and Governance Services Across the Gold Coast, Toowoomba, Brisbane & Queensland
Loginet delivers IT compliance and governance services from our Toowoomba head office and our Bundall office on the Gold Coast, with onsite support across Queensland and service available in other Australian states. Brisbane businesses are supported remotely, with onsite visits when needed. We support IT compliance and governance for businesses across South East Queensland, with managed IT in Toowoomba from our head office, managed IT on the Gold Coast from our Bundall office, and managed IT in Brisbane delivered remotely and on site from our Toowoomba and Bundall teams.
Gold Coast
Our Bundall office supports businesses across Southport, Surfers Paradise, Broadbeach, Robina and the wider Gold Coast.
Toowoomba
Our head office serves Toowoomba and the Darling Downs with local, onsite support.
Brisbane
We support Brisbane businesses remotely, with onsite visits arranged when your project needs them.
Regional Queensland
We provide onsite support across Queensland, with service available in other Australian states.
Why Choose Loginet for IT Compliance and Governance Services
Loginet connects compliance with the IT that delivers it.
- Practical: Controls our engineers can implement.
- Security certified: CEH-certified staff in the team.
- Essential Eight focus: Australian frameworks.
- Local: Toowoomba and Gold Coast offices.
IT Compliance and Governance Services FAQs
Here are straight answers to the questions we hear most. If yours isn’t covered, book a free 30-minute strategy call.
IT governance is the framework of policies, roles and processes that makes sure technology supports business goals and risks are managed.
It depends on your industry, size and customers. Common examples include the Privacy Act, contractual security requirements and the Essential Eight. We help identify what applies.
Yes. We review your controls, close gaps and organise the evidence auditors ask for.
Yes. We develop practical IT and security policies tailored to your business.
The Essential Eight is a set of security strategies from the Australian Signals Directorate. Many customers, insurers and government bodies ask suppliers to align with it.
No. Controls and evidence need regular review. We can provide ongoing compliance support.
Yes. Brisbane businesses are supported remotely, with onsite visits arranged when needed, from our Toowoomba head office and Bundall (Gold Coast) office.
The Privacy Act generally applies to businesses with an annual turnover of more than $3 million, and to some smaller businesses, such as health service providers. Queensland’s Information Privacy Act 2009 mainly applies to Queensland government agencies rather than private businesses. Check your obligations with the OAIC or a legal adviser.
The NDB scheme requires organisations covered by the Privacy Act to notify affected individuals and the OAIC when a data breach is likely to result in serious harm.
It depends on your starting point and obligations. We give you a timeframe after the initial review.
The number of obligations, the size of your environment, how much documentation already exists and whether ongoing reviews are needed all affect cost.
Compliance means meeting specific legal, contractual or industry requirements. Governance is the wider framework of policies, controls and accountability that keeps your business compliant and secure over time, not just at audit time.
Book Your Free 30-Minute Strategy Call
The quickest way to get started is a free 30-minute strategy call. We’ll talk through your setup and goals and give you clear next steps, with no obligation. Prefer to write? Send us a message instead.
Let's talk about your IT
Book a free 30-minute strategy call with our team, or send us a message. No obligation, no hard sell, just straight answers about your IT, cloud and telecom.
Prefer to call?
Sales: Mon–Fri 9am–5pm AEST. Existing clients: 24/7 support on the same number.
Book a free 30-minute call
30 minutes · Video or phone · Times shown in Australia/Brisbane (AEST)
Calendar not loading? Open the booking page in a new tab (opens in a new tab)